The audit log : who did what
"Audit log" page
This page records the actions performed within the Security Center itself. It answers the traceability principle set out by the European personal-data regulation: being able to show who did what.
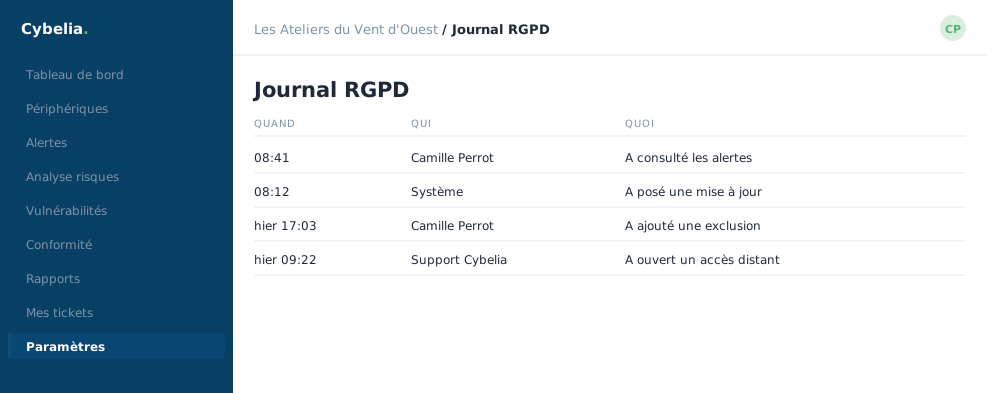 Who did what, and when: including the access opened to Cybelia Cloud support.
What you find there
Each line carries a timestamp, the user, the type of action, a detail, and the address the action came from. The action types are explicit and jargon-free: login, logout, registration, password change, report generation, download, deletion, emailing, user creation, playbook triggering.
How to search
Four filters: by user, you type the start of the email address, by action type, and between two dates. A Reset button clears everything. Results are read page by page, with the total at the top.
This log protects honest people first. When a document disappears or a setting has changed, the question "who?" quickly becomes heavy. Here the answer is written, dated, indisputable, and most often, it clears everybody.
Two logs not to confuse
The audit log traces actions in the Security Center: who logged in, who generated what. The Activity page, seen in the previous chapter, traces what happens on your machines. One speaks of people, the other of computers.
In practice, you come here twice a year: on audit day, and on the day someone genuinely wonders who deleted the March report.
In closing
The log is not there to watch your colleagues: it is there to prove what was done, and by whom, on the day the question arises. It is a requirement of European regulation, and a protection for everyone.
Commenting is not enabled on this course.